What if one of the biggest weaknesses in an organisation’s access controls is the person trusted with the password?
Research from UK fraud prevention service Cifas raises an uncomfortable question about how employees view access to company systems.
Its Workplace Fraud Trends research, based on a survey of 2,000 UK employees working for organisations with more than 1,000 staff, found that 13% said they had either sold company login details to a former colleague or knew someone who had done so in the previous 12 months. A further 13% believed selling access to company systems could be justified.
For organisations investing heavily in cyber security, identity management and access controls, these findings highlight an important aspect of insider risk: a complacent, careless or cynical culture can be a major vulnerability.
Insider Risk Does Not Always Begin with Malicious Intent
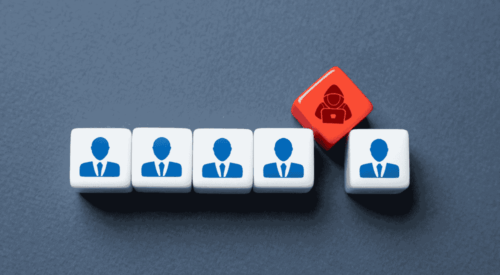
When organisations think about insider threats, attention often first turns to the malicious or compromised employee deliberately stealing information, committing fraud or working on behalf of an external actor. But much insider risk starts with naive and/or inadvertently risky behaviour such as clicking on a phishing email. Some also happens because staff are just trying to get business done.
Employees may share credentials because they believe they are helping a colleague, circumvent controls because they make their job easier, or provide access without fully appreciating the potential consequences. At the same time, others may be motivated by stress, financial pressure or sometimes with nakedly malign intent to deliberately exploit the access their organisation has entrusted to them.
In each case, legitimate access can provide a route around security controls designed primarily to keep external attackers out.
When Risky Behaviour Becomes Normalised
Perhaps one of the most significant aspects of the Cifas research is not simply that credential selling occurs, but the frequency and apparent level of acceptance surrounding it.
The findings raise wider questions about organisational culture and whether employees fully understand their individual responsibility for protecting access to company systems.
Bill Trent, Managing Director at GSA Global, says: “The figures are concerning not simply because people are prepared to share or sell access, but because they suggest some employees may not recognise the seriousness of doing so. Insider risk is as much about culture and behaviour as it is about technology. Organisations need to understand why people make these decisions, identify where vulnerabilities may be developing and create an environment where concerns can be recognised and addressed before they become incidents.”
Technology can restrict access and detect unusual behaviour, but it cannot address the problem alone. It is not enough for staff to be told what the rules for system access are; but why these controls are in place and the potential consequences when trusted access is misused.
The Risk Does Not End When Someone Leaves
The specific reference to former colleagues in the Cifas findings is also significant.
An organisation may revoke a departing employee’s credentials, but former employees can retain relationships with colleagues who still have legitimate access to systems and information.
Traditional leaver processes may not address all potential risks. Effective insider risk management needs to consider culture, behaviours, relationships and changes in circumstances throughout the employee lifecycle, rather than treating vetting and access management as one-off activities.
Insider Risk is More Than Cyber Security
Credential misuse demonstrates why insider risk should not be the exclusive responsibility of a non-technical security & investigations, cyber security or HR function. Effective Insider Risk Management (IRM) requires technology to be combined with appropriate governance, personnel security, awareness, reporting mechanisms and an organisational culture in which employees understand their responsibilities.
It also means recognising that insider risk exists on a spectrum, from inadvertent actions and poor security behaviours through to deliberate fraud, coercion or sophisticated external compromise.
Ultimately, every organisation needs to trust people with access to information, systems and assets. The challenge is ensuring that trust is supported by proportionate controls and a culture in which access is understood as a responsibility rather than simply a convenience.
The Cifas findings provide a useful reminder that insider risk does not always begin with a sophisticated attack or deliberate act of espionage. Sometimes it starts with something much simpler: a trusted individual deciding that sharing access does not really matter.
How GSA Global Can Help
GSA Global helps organisations identify, assess, mitigate and manage insider-related risks before they result in material harm to people, organisational assets, operations or reputation.
Our Insider Risk Management team brings exceptional expertise and insights from working with leading firms and government organisations. We do this by bringing together human, cyber and physical security expertise, with broader organisational and business risk management insight. GSA help organisations improve vetting, culture and whistleblowing arrangements, detection and response, and the many other facets of an effective insider risk management programme. We also investigate major incidents.
Importantly, we help organisations assess their exposure, strengthen governance and develop effective IRM programmes that deal with the growth of and evolution in insider related risks. These include new risks include risks presented by insiders in critical third parties and non-human agentic-AI insiders.